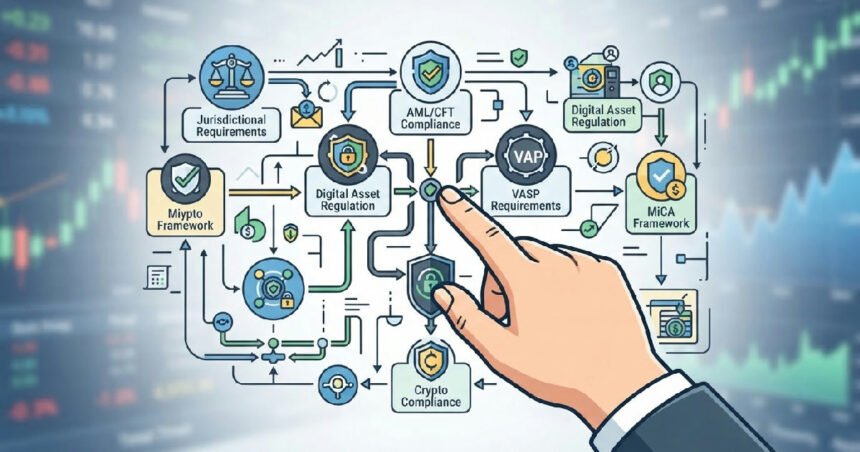
Understanding how to navigate crypto regulations for your business is paramount in today’s complex digital asset landscape. It demands a detailed understanding of varying jurisdictional requirements, precise classification of digital assets, and the implementation of robust Anti-Money Laundering (AML) and Counter-Terrorist Financing (CFT) compliance programs.
The regulatory environment remains fluid, shifting significantly across regions and asset types, making a proactive, risk-based strategy essential for adherence to both global and local standards.
How to navigate crypto regulations for understanding
This evolving framework requires businesses to stay informed about key definitions and the mandates of influential regulatory bodies. Missteps can lead to significant penalties, reputational damage, and operational disruptions. So, having a clear roadmap for compliance isn’t just good practice; it’s a necessity for sustained growth.
To effectively manage crypto regulations, businesses must first grasp core terminology and the roles of principal regulatory bodies. These definitions form the bedrock of compliance frameworks worldwide.
A **Virtual Asset (VA)**, as defined by the Financial Action Task Force (FATF), represents any digital value that can be digitally traded, transferred, or used for payment, excluding digital representations of fiat currencies. These assets, typically blockchain-based, are used for purchasing, investment, or trading, and can signify ownership or rights.
A **Virtual Asset Service Provider (VASP)** is any entity that conducts specific activities on behalf of others as a business. This includes exchanging VAs for fiat or other VAs, transferring VAs, or safeguarding these assets. The FATF extended AML/CFT obligations to VASPs in its 2019 update to Recommendation 15.
In Europe, the Markets in Crypto-Assets Regulation (MiCA) refers to these entities as Crypto-Asset Service Providers (CASPs).
Critical to this framework are **Anti-Money Laundering (AML)** and **Counter-Terrorist Financing (CFT)** regulations. These procedures prevent illicit funds from entering the legitimate financial system and stop the financing of terrorist activities. VASPs must implement preventive measures akin to traditional financial institutions, including customer due diligence, record-keeping, and reporting suspicious transactions.
**Know Your Customer (KYC)** is a vital AML component, requiring businesses to verify customer identities to assess potential risks. VASPs must screen and verify customers when accounts are opened. This process helps to mitigate the risks associated with anonymity in the digital asset space.
Major Regulatory Bodies in the Crypto Space
Several intergovernmental and national bodies play crucial roles in shaping the crypto regulatory landscape. Their mandates often overlap but also present unique jurisdictional requirements.
Asset Classification and Regulatory Scope for Businesses
The regulatory treatment of any crypto asset hinges significantly on its classification, a critical factor that varies substantially by jurisdiction. This inherent variability means that understanding these distinctions is not merely beneficial but fundamental for any business operating within the digital asset ecosystem.
Proper classification directly determines which regulatory frameworks apply, influencing everything from licensing requirements and operational procedures to financial reporting obligations and tax implications. Consequently, accurate assessment of an asset’s nature is the first step towards establishing a compliant and sustainable business model in this complex domain.
Misclassification can lead to severe penalties, including hefty fines, legal disputes, and significant reputational damage, underscoring the necessity of a meticulous approach. For instance, an asset classified as a security in one region might be deemed a commodity in another, leading to divergent compliance pathways.
This jurisdictional divergence necessitates a sophisticated understanding of both local statutes and international guidelines to avoid regulatory pitfalls. Businesses must invest in thorough legal and compliance analyses to navigate these varied landscapes effectively, ensuring their operations align with the specific demands of each market they engage with.
U.S. Classification Approach (SEC/CFTC)
In the U.S., the Securities and Exchange Commission (SEC) and the Commodity Futures Trading Commission (CFTC) primarily govern crypto assets. The SEC uses the Howey Test to determine if a crypto asset is an “investment contract” and thus a security. An investment contract exists with an investment of money in a common enterprise, with a reasonable expectation of profits derived from others’ efforts.
The CFTC typically classifies certain crypto assets, such as Bitcoin (BTC) and Ethereum (ETH), as commodities. Other examples of digital commodities include Solana (SOL), Cardano (ADA), XRP, Dogecoin (DOGE), Polkadot (DOT), Avalanche (AVAX), Chainlink (LINK), and Litecoin (LTC). These assets are intrinsically linked to a functional crypto system rather than relying on managerial efforts for value.
Digital Collectibles, like many Non-Fungible Tokens (NFTs) and memecoins, are generally not treated as securities if their value stems from artistic, entertainment, or cultural significance and supply-and-demand dynamics, without conveying rights to future profits. Digital Tools, performing practical functions like membership proof, also typically avoid security classification.
Stablecoins, designed to maintain a stable value, have varied classifications depending on their structure and use, prompting guidance from both the SEC and CFTC.
EU Classification Under MiCA
The European Union’s MiCA framework offers a structured approach to classification, ensuring legal certainty and consumer protection across member states. MiCA categorizes crypto assets into E-money Tokens (EMTs), Asset-Referenced Tokens (ARTs), and Utility Tokens.
EMTs are stablecoins pegged to a single fiat currency, while ARTs stabilize their value by referencing other values or rights, or a combination including official currencies. Utility Tokens are designed to provide access to specific goods or services. MiCA specifically covers crypto assets not already regulated by existing EU financial services legislation, creating a harmonized approach.
Addressing Specific Asset and Activity Challenges
Beyond broad classifications, certain digital asset types and activities present unique regulatory hurdles. Businesses must account for these nuances to maintain compliance.
Non-Fungible Tokens (NFTs) are generally not specifically regulated, but their legal status continues to evolve. The FATF suggests regulating NFTs as virtual assets if they function as payment or investment instruments, rather than purely as collectibles. Platforms facilitating NFT exchanges, especially those acting as investment or payment vehicles, might therefore qualify as VASPs.
Decentralized Finance (DeFi) platforms pose significant compliance challenges. Their decentralized architecture, lack of a central governing authority, and emphasis on user anonymity create complexities for regulators. Concerns about illicit activities, fraud, and security vulnerabilities mean DeFi platforms are under increasing scrutiny. Implementing KYC/AML in DeFi often clashes with the fundamental ethos of decentralization.
Strategic Compliance for Digital Asset Businesses
For any business operating in the crypto sector, establishing a robust and adaptable compliance framework is non-negotiable. This involves continuous monitoring and proactive engagement with regulatory developments.
A multi-faceted approach is essential for how to navigate crypto regulations for long-term sustainability. Start by conducting a thorough risk assessment of all your digital asset activities and offerings. Identify which jurisdictions apply to your operations and what specific licenses or registrations are required. This due diligence prevents potential legal exposure down the line.
Next, implement comprehensive AML/CFT and KYC programs tailored to your risk profile. This includes verifying customer identities at onboarding, monitoring transactions for suspicious activity, and maintaining meticulous records. Training staff on these procedures and keeping them updated on regulatory changes are also critical components. Consider leveraging technology solutions that automate some of these compliance tasks.
Lastly, establish clear internal policies and procedures for handling customer complaints, data privacy, and security breaches. Regular internal audits and external reviews can help identify gaps in your compliance framework before they become major issues. Staying informed about legislative changes, like new guidance from the FCA or updates to MiCA, is an ongoing responsibility.
What is the primary concern of crypto regulators?
The primary concern for crypto regulators is typically to prevent illicit activities such as money laundering and terrorist financing, protect consumers and investors, and ensure market integrity and financial stability within the digital asset ecosystem.
How do global crypto regulations differ for businesses?
Global crypto regulations differ significantly, particularly in asset classification, licensing requirements, and the scope of AML/CFT obligations. The U.S. relies on the SEC and CFTC, while the EU uses the unified MiCA framework, each with distinct approaches to digital assets.
Why is asset classification important for crypto businesses?
Asset classification is crucial because it dictates which regulatory body has jurisdiction and what specific rules apply to an asset. Misclassifying an asset can lead to non-compliance, hefty fines, and legal challenges, impacting a business’s ability to operate legally.